Overview

Certification audit and IS audit (IS-Revision) according to BSI IT-Grundschutz

Is a certification date coming up, or does a client require certification based on IT-Grundschutz or an IS audit (IS-Revision)? We clarify the required evidence and audit using the appropriate procedure – independent and technically sound.

Free of charge and without obligation.

  • BSI-certified for IS consulting and IS audit
  • BSI audit team leaders for ISO 27001 on the basis of IT-Grundschutz
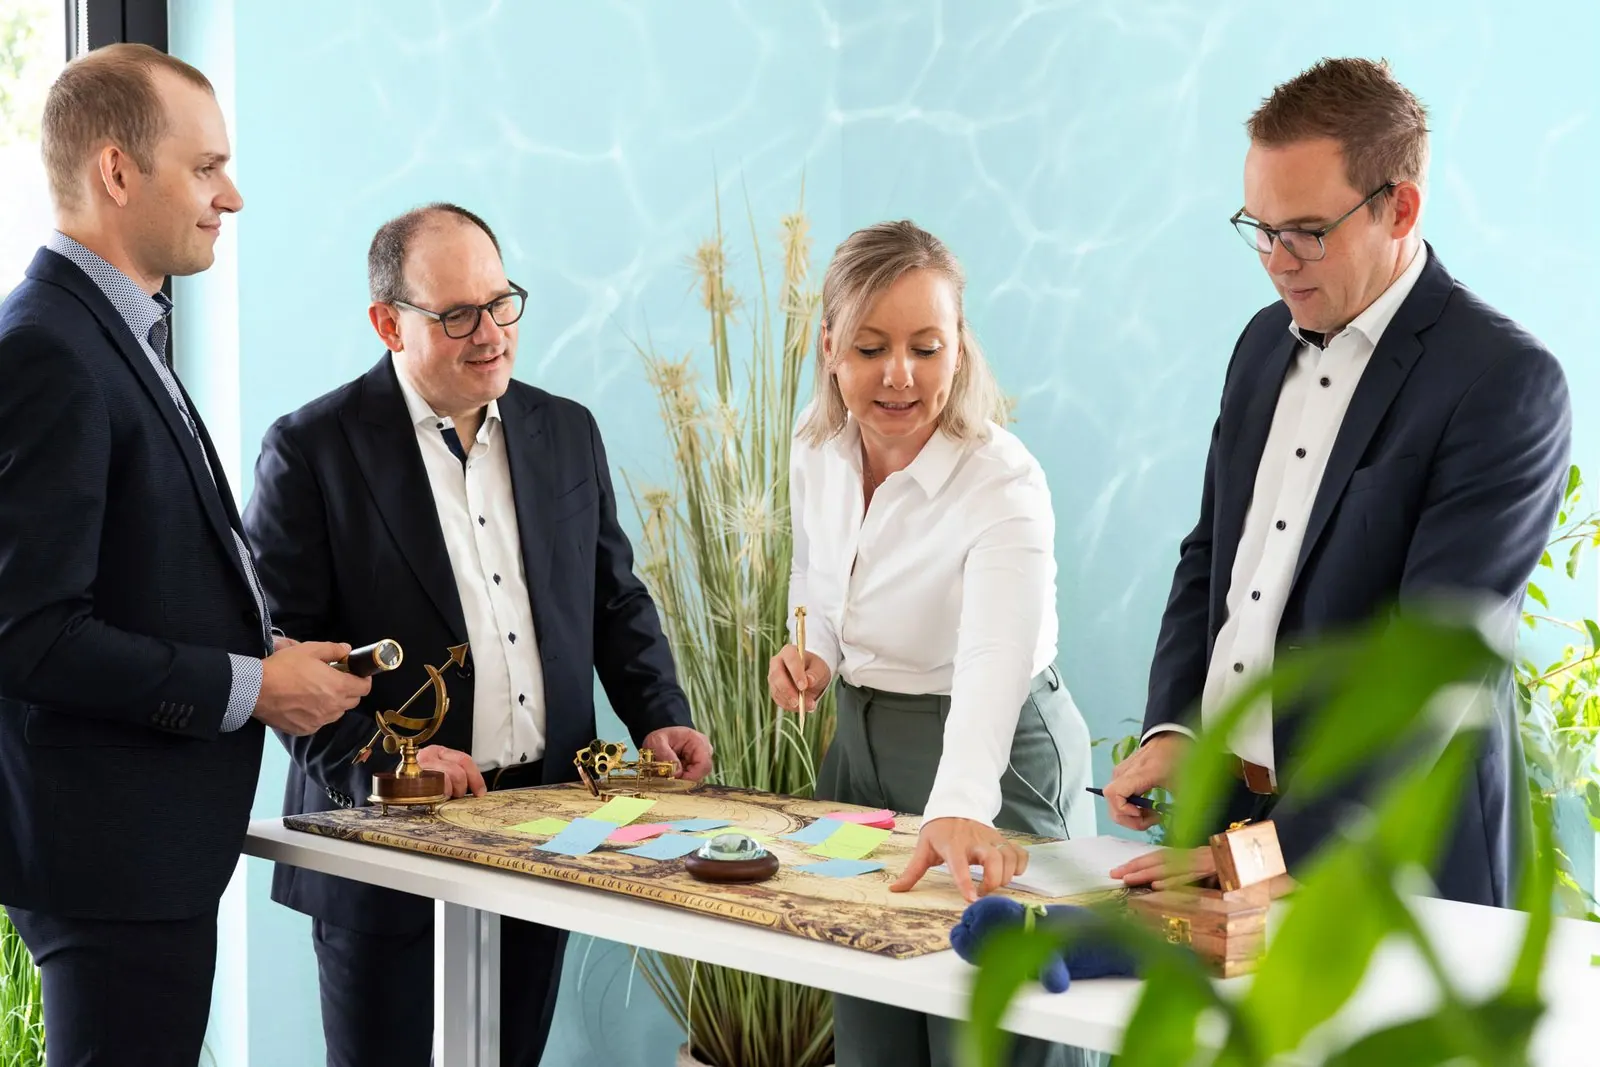
A secuvera consultant explaining the joint plan to her team at a map
Certification based on IT-Grundschutz: independent and comprehensible.

Your situation

Do you want your ISMS (information security management system) according to BSI IT-Grundschutz to be certified or reviewed by an IS audit (IS-Revision), and are you looking for experienced auditors?

Is a certification or recertification date coming up, does a client or a supervisory authority require specific evidence, or do you want your organisation's security level assessed independently? Often it is still unclear which procedure and which audit scope are appropriate.

If your ISMS follows BSI IT-Grundschutz, certification by the BSI or an IS audit (IS-Revision) without a certificate are both options.

This is where we start: first we clarify who requires which evidence, and then we define an appropriate audit scope. The audit is carried out by our certified auditors for ISO 27001 based on IT-Grundschutz and our IS auditors. Because we also carry out technical security tests, our auditors audit with technical expertise. We allow enough time so that findings are comprehensible and genuinely help you from a technical point of view.

For setting up your ISMS according to BSI IT-Grundschutz, we offer our BSI IT-Grundschutz consulting. Does your ISMS follow ISO 27001? You will find consulting and certification audits for it under ISO 27001: consulting and audit.

Testing portfolio

Which audits we carry out

For organisations that already operate an ISMS and need the evidence.

BSI IT-Grundschutz

  • Certification audit ISO 27001 based on IT-Grundschutz
  • Attestation for basic protection (Basis-Absicherung) according to IT-Grundschutz
  • IS audit (IS-Revision) and short IS audit (IS-Kurzrevision) according to the BSI guideline
  • Internal audits for preparation

Services & results

Two audit procedures, comprehensible results

For BSI IT-Grundschutz, you receive initial and recertification audits according to ISO 27001 based on IT-Grundschutz, as well as IS audits (IS-Revision), carried out by certified auditors and IS auditors. In every procedure, you receive a meaningful report with comprehensible findings.

Each of these types of evidence follows its own procedure. We first clarify which evidence you need and then audit according to the respective prescribed scheme.

Certification according to BSI IT-Grundschutz

Do you need to have your organisation or a part of it certified according to BSI IT-Grundschutz? Our experienced, certified auditors for ISO 27001 based on IT-Grundschutz carry out the audit and submit the audit report to the BSI, which decides on the certification.

According to the BSI milestone plan (as of October 2026), certification applications based on Grundschutz++ will be possible from 1 January 2027; training for GS++ audit team leaders begins in the first quarter of 2027. Certifiability under the previous IT-Grundschutz ends on 30 November 2031. For a new ISMS, we therefore recommend Grundschutz++ and plan the certification date according to the BSI procedure that applies by then. If a client requires a certificate at short notice, certification under the previous IT-Grundschutz can be the necessary interim step. Existing implementations can continue to be certified until 30 November 2031.

Audit report for the BSI

A meaningful audit report with comprehensible findings from which you also gain technical insight.
IS audit according to the BSI guideline

Does your ISMS have to meet the requirements of BSI IT-Grundschutz but does not need certification? Then an IS audit (IS-Revision) according to the BSI's IS audit guideline (Leitfaden IS-Revision) independently determines the security level achieved and shows gaps and opportunities for improvement. Which type of audit is appropriate depends on the audit objective and requirements: the short IS audit (IS-Kurzrevision) gives an overview of the whole institution with little effort, the cross-sectional IS audit (IS-Querschnittsrevision) samples all layers of IT-Grundschutz, and the partial IS audit (IS-Partialrevision) examines a defined area in greater depth. Our IS auditors provide:

  • an audit along the topics described in the guideline
  • a comprehensible assessment related to your processes and your documentation
  • visibility of critical areas requiring urgent action
  • prioritised recommendations for the next steps

IS audit report

An assessment of the security level achieved, with prioritised recommendations.

Our expertise

Since December 2011, secuvera has been certified by the BSI (Federal Office for Information Security) as an IT security service provider for IS audit (IS-Revision) and IS consulting. For BSI IT-Grundschutz, we have several experienced, certified auditors for ISO 27001 based on IT-Grundschutz in-house, as well as IS auditors.

secuvera is also certified by the BSI as an IT security service provider for IS penetration testing. Because audits and penetration tests come from one organisation, you receive coordinated organisational and technical audits from a single source.

BSI-certified IT security service provider

IS consulting and IS audit: independently verified

Company certification by the BSI for our services in IS consulting and IS audit (IS-Revision). It applies to secuvera as a service provider, not to individuals.

View certification for IS consulting and IS audit

BSI-certified audit team leaders

Personal certification: several of our colleagues are certified by the BSI as audit team leaders for ISO 27001 audits based on IT-Grundschutz.

View audit team leaders in the BSI register

Getting started

Defining the audit type and procedure

Clarify the evidence you need

Tell us your scope and the planned certification or audit date. Existing certificates and previous audit findings are also part of the preparation.

Agree audit procedure and responsibilities

We discuss the appropriate audit type, the documents required and the next steps.

Agree on an audit or IS audit
The points of a pair of dividers resting on coloured sticky notes above a map
Audit type chosen to match your evidence goal.

Audit and certification decision

The audit and the certification decision are separate. The scope of the audit and responsibilities are agreed according to the evidence required.

Your questions about IT-Grundschutz certification and IS audit (IS-Revision)

What is the difference between an IS audit and a certification?

An IS audit (IS-Revision) assesses the security level according to the BSI's IS audit guideline (Leitfaden IS-Revision) and does not require certification. Depending on the audit objective, it is a short IS audit (IS-Kurzrevision), a cross-sectional IS audit (IS-Querschnittsrevision) or a partial IS audit (IS-Partialrevision); the result is an audit report with recommendations. A certification, by contrast, follows the BSI's procedure.

Do you carry out audits according to BSI IT-Grundschutz?

Yes. Our team includes certified auditors for ISO 27001 based on IT-Grundschutz as well as IS auditors. Whether a certification or an IS audit (IS-Revision) is appropriate depends on the evidence you need.

Do you carry out audits based on IT-Grundschutz?

Yes. For planning, the existing certificate, scope, previous findings and the intended date are important. We coordinate the conduct of the audit with you and the BSI.

Articles on this topic (in German)

All 37 articles on the topic (in German)

How can we support you with certification and IS audit?

Tell us the evidence you need, the audit or certification scope, any existing certificates, your target date and, if applicable, previous findings. From this we clarify the type of audit, the scope and responsibilities.

Discuss your audit