Overview

BSI IT-Grundschutz consulting for a workable ISMS (information security management system)

You are setting up an ISMS (information security management system) under BSI Grundschutz from scratch, or continuing an existing IT-Grundschutz ISMS? For a new set-up, we recommend Grundschutz++ (BSI Standard 300-1). We help you develop an existing ISMS under classic IT-Grundschutz (BSI Standard 200-2) in a planned way and prepare the decision on whether to migrate.

Free of charge and non-binding.

  • BSI-certified IT-Grundschutz Consultants in our team
  • BSI-certified for IS consulting and IS audit (IS-Revision)
  • BSI-certified audit team leaders for ISO 27001 on the basis of IT-Grundschutz
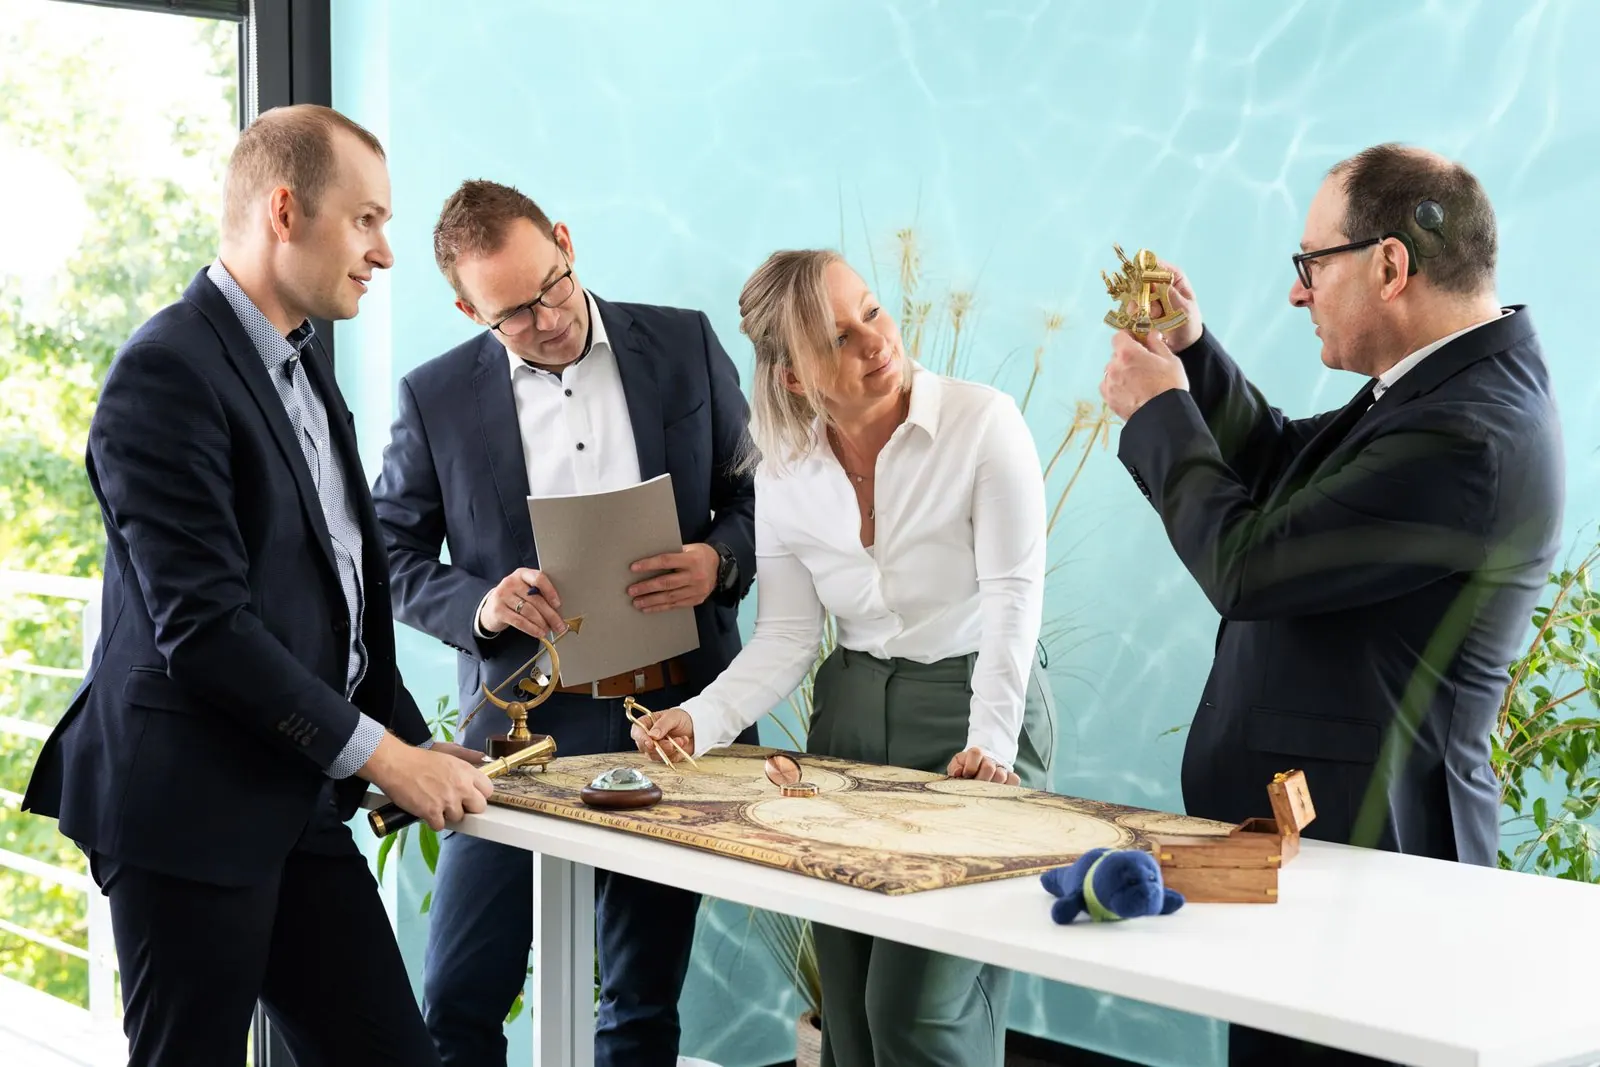
Four members of the secuvera team planning a project at a map with navigation instruments
BSI Grundschutz that works in day-to-day practice, together with your team.

Your situation

Are you building an ISMS, or do you already run one based on IT-Grundschutz?

Your starting point decides which path makes sense. We distinguish between two situations.

New set-up: You are starting an ISMS because a client, a supervisory authority or your management requires it. Here we recommend aligning with Grundschutz++ and BSI Standard 300-1; a classic new set-up under BSI Standard 200-2 is no longer our standard recommendation. Together with you, we determine the business processes you secure first and build a traceable ISMS around them, including structures for evidence and implementation.

Existing ISMS: You already work under IT-Grundschutz and are asking what Grundschutz++ means for your processes, documents and certification. We recommend not migrating without careful consideration. First we assess the maturity and currency of your ISMS, the differences between 200-2 and 300-1, your certification requirements and the likely effort. This results in a realistic approach, ranging from further development within the current framework to a planned migration.

Classic IT-Grundschutz remains relevant where existing requirements, ongoing certifications or client specifications call for it. According to the BSI milestone plan, certification applications based on Grundschutz++ are possible from 1 January 2027; certifiability under the current IT-Grundschutz is due to end on 30 November 2031. Grundschutz++ is not yet established in all its components: according to the BSI, the early adopter phase begins in the first quarter of 2027 and ends on 31 December 2027. We take this into account in our planning and state openly which decisions still depend on further developments. If your client requires certification under ISO/IEC 27001 with no connection to IT-Grundschutz, ISO 27001 consulting is the right path.

How you decide whether and when a migration makes sense is described in our article Grundschutz++: Getting started and migrating under BSI 300-1 (in German).

We have been working with ISMS since the days of the BSI IT Security Handbook (BSI-Sicherheitshandbuch). In the BSI directory, secuvera is listed under the ID BSI-APS-9002 as a certified IT security service provider for IS audit (IS-Revision) and IS consulting. If the audit itself is due, our auditors carry it out as part of Grundschutz certification or IS audit (IS-Revision) – but not for an organisation we have previously advised. If you first need an information security concept for individual systems or areas, we support you with creating security concepts. For projects under the Bundeswehr's IT-Grundschutz or involving classified information, we create audit-ready security concepts.

If your client does not require a Grundschutz certificate, an ISMS under ISO 27001 may also be the appropriate evidence target. Together with you, we assess which path fits your requirements.
Services & results

From your starting point to an ISMS that your own people can run

You get an ISMS (information security management system) based on BSI Grundschutz that fits your processes: either newly built on Grundschutz++ or developed in a planned way from an existing IT-Grundschutz ISMS. The outcome is a reasoned decision on which evidence you aim for and when, plus documentation that your team can maintain itself.

We do not implement the BSI standards slavishly but adapt them to your organisation. The aim is a state that is workable and formally correct at the same time. We prepare decisions with you; you make them, and you remain responsible for your ISMS.

Clarify the starting point and the evidence goal

First we clarify whether you are building from scratch or developing an existing ISMS, which evidence is required (certification under ISO 27001 based on Grundschutz++ or IT-Grundschutz, attestation or IS audit (IS-Revision) without a certificate) and which business processes or information domain are in focus.

For the initial assessment, a workshop of one to two days with your subject-matter contacts is often enough.

Your approach

A reasoned basis for decision with route, evidence goal and schedule.

Choose the route: new build or migration

For a new build, we orient ourselves towards Grundschutz++ and BSI Standard 300-1: we identify the relevant business processes, prioritise them and first work out one area at the required depth. You use it to try out methodology, tools and evidence management before further areas follow.

For an existing ISMS, we assess maturity, compare the requirements of 200-2 and 300-1, and check which structures, risk analyses and evidence can be carried over. The result is a set of options with effort estimates that take your certification cycle and your tools into account.

Develop methodology and documents together

We do not rely on off-the-shelf documents: we bring proven content from many projects, but we adapt every document to your actual processes together with your responsible staff. We include existing security concepts and documents.

This produces documentation that is actually used – and does not disappear into a drawer after the audit. Depending on the methodology, this includes:

  • Recording business processes and their resources (Grundschutz++)
  • Implementing the requirements of the user catalogue (Grundschutz++)
  • Risk identification, assessment and treatment according to the BSI minimum criteria (Grundschutz++)
  • Structure analysis, protection requirements assessment, modelling and IT-Grundschutz check (IT-Grundschutz)
  • Risk analysis according to BSI Standard 200-3 (IT-Grundschutz)

Your ISMS documentation

Reference documents and processes that describe your actual organisation and that your responsible staff can keep up to date.

Prepare for the attestation or certification

Applications for certification under Grundschutz++ are possible from 1 January 2027; we prepare you for the evidence you have agreed. Our BSI-certified IT-Grundschutz Consultants support you in this. Because our team also includes BSI-certified audit team leaders for ISO 27001 based on IT-Grundschutz, the perspective of audit practice feeds into the preparation.

The audit itself is carried out by an independent body: under the certification scheme, consulting and certification audit cannot be combined for the same organisation.

Handover: your ISMS runs without us

An ISMS must be maintained by your own responsible staff and employees. We have reached our goal when your organisation no longer needs our support and the ISMS works as implemented.

If you still want ongoing support, an external information security officer from secuvera can take on this role.

Our expertise

We have worked with information security management systems since the days of the BSI security manual – a Computerwoche article from 1993 documents this. We have advised on IT security since 1988, and since December 2011 as a BSI-certified IT security service provider.

Our team includes BSI-certified IT-Grundschutz Consultants and BSI-certified audit team leaders for ISO 27001 based on IT-Grundschutz. Many of the organisations we have supported are certified today – mostly because they prepared well with our support, in some cases after an audit by our auditors.

Our colleague Daniel Künkel contributed to the methodology of Grundschutz++ as a co-editor. Together with Reto Lorenz, he analysed the methodological consequences in a specialist article in the magazine IT-Sicherheit. This experience informs our consulting.

BSI-certified IT-Grundschutz Consultant

BSI-certified IT-Grundschutz Consultants

Several of our cybersecurity consultants are certified by the BSI as IT-Grundschutz Consultants. This personal qualification complements secuvera's BSI certification for IS consulting.

View personal qualifications in the BSI register
BSI-certified IT security service provider

IS consulting and IS audit: independently verified

secuvera is certified by the BSI (Federal Office for Information Security) as an IT security service provider for IS consulting and IS audit (IS-Revision). This evidence covers our consulting and audit services; certification decisions are made by the responsible certification bodies.

View certification for IS consulting and IS audit

BSI-certified audit team leaders

Several of our colleagues are certified by the BSI as audit team leaders for ISO 27001 audits on the basis of IT-Grundschutz. The qualification concerns conducting the audits; the certification decision remains with the BSI.

View audit team leaders in the BSI register

Supporting TDT AG through to IT-Grundschutz certification

We supported the manufacturer of routers and gateways in implementing the IT-Grundschutz requirements until it was ready for certification. The BSI certified the information domain to ISO 27001 on the basis of IT-Grundschutz.

Read project report

Getting started

Clarifying your starting point and evidence goal

Setting up from scratch or an existing ISMS?

Describe your organisation, your most important business processes and, if available, your existing ISMS, your security concepts and certification dates. For a new setup, we work with you to prioritise the processes for getting started. For an existing ISMS, we assess how up to date it is, the evidence and the certification cycle, and compare them with the new methodology.

Clarify your starting point
Dividers and compass on a historical world map
Information domain clearly defined, effort realistically planned.

New setup, migration, attestation and certification are different goals

A new setup with Grundschutz++, migration of an existing ISMS, an attestation for the Basis-Absicherung and ISO 27001 certification based on IT-Grundschutz are different goals, each with its own procedure. Grundschutz++ is not the same as an already established certification: applications are only possible from 1 January 2027. At the start, we clarify which evidence you need and when.

Questions about implementing IT-Grundschutz

Should we start with Grundschutz++?

If you are setting up a new ISMS based on BSI Grundschutz, you should in principle follow Grundschutz++ and BSI Standard 300-1; a classic new setup according to 200-2 is no longer our standard recommendation. The exception is specific requirements, for example when a client demands evidence under the previous procedure at short notice. Grundschutz++ is not yet established in all its components; we take this into account in the planning.

Is the Basis-Absicherung still a suitable starting point?

The Basis-Absicherung belongs to the previous methodology under 200-2. For a new setup, we now recommend Grundschutz++. If you already work with the Basis-Absicherung or need an attestation for it, you can continue with it; whether and when a switch makes sense, we clarify when assessing your existing ISMS.

Will we receive ready-made Grundschutz documents?

We bring experience and tested approaches, but we adapt the documents to your information domain. A document taken over unchanged rarely describes your actual processes. Working on them together is meant to enable your employees to maintain the documents themselves later.

Is an attestation for Basic Protection (Basis-Absicherung) the same as a certification?

No. The attestation confirms the audited implementation of Basic Protection. An ISO 27001 certification on the basis of IT-Grundschutz follows a different procedure. We clarify the required evidence objective before preparation begins.

Can secuvera advise us and later also certify us?

Not both for the same organisation. Under the certification scheme, consulting or coaching and the certification audit cannot be combined. You decide whether we prepare you for the audit or carry out the audit.

Does an existing ISO 27001 certificate help when moving to BSI Grundschutz?

It makes preparation easier, but it is not sufficient. The ISMS documents have to be prepared differently for IT-Grundschutz. How quickly this can be done depends on your existing ISMS; we clarify this in the initial consultation.

How do we decide whether and when to migrate?

Together with you, we assess the maturity of your ISMS, the certification cycle, existing evidence and tools, and compare the effort of the options. In doing so, we separate what the BSI has already defined from questions that are still open. The decision is yours; we prepare it so that you can justify it.

Articles on this topic (in German)

All 36 articles on the topic (in German)

Older articles reflect the legal situation at the time of publication. The sections above summarise the current situation.

How can we support you with Grundschutz?

Whether you need to set up an ISMS from scratch or decide on a migration: we discuss your starting point and check which route and which existing documents will support it.

Discuss IT-Grundschutz