Overview

ISO 27001: consulting and certification audit for your ISMS

You want to improve your information security level by introducing an ISMS (information security management system) to ISO 27001, demonstrate it to customers, or have your ISMS certified?

Free of charge and without obligation.

  • Our own ISO 27001-certified ISMS
  • ISO 27001 Lead Auditors on the team
  • BSI-certified for IS consulting and IS audit
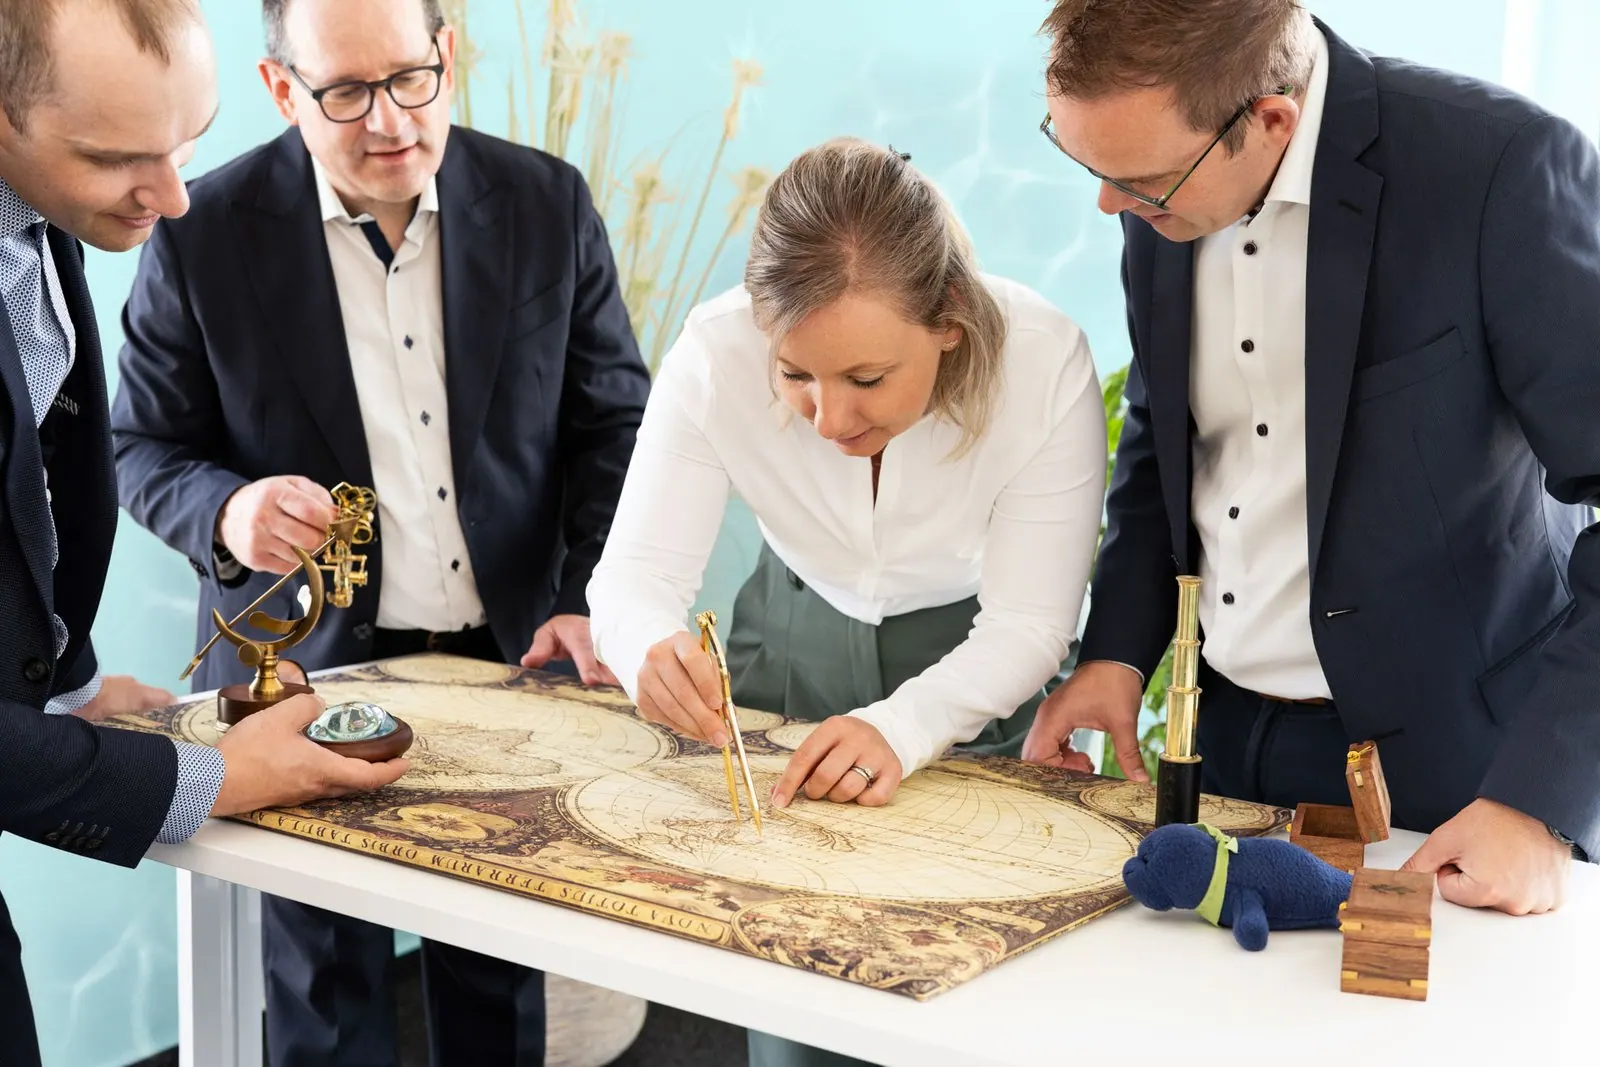
Four members of the secuvera team following work with dividers on a map
ISO 27001 consulting: on a clear course from gap analysis to audit.

Your situation

You are expected to introduce an ISMS to ISO 27001, demonstrate it to clients or have it certified?

A client requires an ISO 27001 certificate, you are a network operator subject to the IT security catalogue under the EnWG (German Energy Industry Act), or your existing ISMS needs to pass its next audit. NIS2 can also be a reason for an ISMS to ISO 27001. You may already have some individual policies – but scope, risk management and responsibilities do not yet work together.

ISO/IEC 27001 only helps to a limited extent here: it is compact and describes security measures only in broad terms. Your organisation has to decide for itself how to assess risks, when to accept a risk and how to implement measures appropriately. Generic templates do not answer these questions.

This is where we start: in ISMS consulting, we work with you to develop an approach that fits your processes, and we support all phases – from the introductory workshop through risk management to the internal audit and support during the certification audit. If your ISMS is already in place, our ISO 27001 lead auditors also carry out initial and recertification audits, together with several partner certification bodies. If you already work to IT-Grundschutz or your client requires it, BSI IT-Grundschutz consulting is a better fit. If you lack a dedicated person to run the ISMS day to day, an external information security officer can take this on. We have been advising on IT security since 1988. In the BSI directory (in German), secuvera is listed under the ID BSI-APS-9002 as a certified IT security service provider for IS audit (IS-Revision) and IS consulting.

If you tend to follow the BSI standards, an ISMS based on IT-Grundschutz may be the better choice. We clarify with you which route fits your evidence goal.

Getting started in one day

1-day workshop: Where does your ISMS stand?

On site or by video conference, we review scope, policies and management processes with you. You get a basis for deciding on your ISMS project.

  • Result: A first indication of which topics are well covered and where improvement is needed, with an estimate of implementation time, effort and costs.
  • Scope: Selected, representative topic areas. The gap analysis follows for a reliable assessment of all standard requirements.

Prefer to talk first? The initial consultation is free of charge and non-binding.

Fixed price

€1,500

net, one day on site or by video conference

Scope of services

How we support you with ISO 27001

Individually or as continuous support – depending on your organisation's starting point.

Implementation and further development

  • Introductory workshops and gap analyses
  • Development of tailored management processes
  • Development and support of risk management
  • Drafting and coordination of policies
  • Project planning and management
  • Awareness training

Audit and evidence

Sector requirements

Services & results

Your ISMS to ISO 27001 – from the start to the certification audit

You get an ISMS to ISO/IEC 27001:2022 that fits your processes: from an introductory workshop or a gap analysis, through scope, risk management and policies, to the internal audit before certification. How long implementation takes depends on the scope, your existing processes and your own involvement. Once your ISMS is in place, our ISO 27001 lead auditors carry out initial and recertification audits together with partner certification bodies. Our own ISMS is certified to ISO/IEC 27001:2022.

We integrate the management system processes into your existing workflows wherever possible instead of building a parallel system. The requirements of the standard are met, and the specifics of your organisation are taken into account.

Getting started: workshop or gap analysis

To decide whether and how to introduce an ISMS, a one-day workshop on site or by video conference is often enough. We explain the standard and possible approaches, have you present your company and your processes, and review selected, representative topics.

If you need reliable knowledge of which requirements of the standard are already met, a gap analysis is the right starting point.

Initial indication

Which topics you already handle well, where there is room for improvement – and an indication of implementation time, effort and costs.
Scope and risk management

Together with you, we define the scope (clause 4 "Context of the organization") and introduce risk management that fits your organisation: identifying, assessing and treating risks to information and the business processes that depend on it – with regard to confidentiality, integrity and availability (clauses 6.1.2 information security risk assessment and 6.1.3 information security risk treatment).

Your management sets the criteria for risk assessment and risk acceptance; we develop them with you and support the first cycles.

Management processes and policies

We develop tailored management processes, draft policies – from the information security policy (clause 5.2) to the controls in Annex A and the Statement of Applicability – and agree them with your responsible staff. We integrate the new management system processes into your existing workflows wherever possible.

On request, we take on project planning and management and run awareness training for your employees.

Including sector requirements

Many sectors supplement ISO 27001 with their own standards. These cannot be certified and are not a general requirement for an ISMS, but they may be binding for you. We analyse which of them apply to you.

For network operators, we build the ISMS in line with the IT Security Catalogue under Section 11(1a) EnWG.

Internal audits and audit preparation

Before certification, our auditors – including ISO 27001 Lead Auditors – review your ISMS in an internal audit under clause 9.2, with a preceding document review and a report checked by an expert not involved in the audit. The results feed into the management review under clause 9.3. We support you during the external audit.

If your auditor also requires technical evidence, we carry out a penetration test for ISO 27001 audits.

Audit-ready

Documented findings from the internal audit and a list of the points still to be addressed before the certification audit.

ISO 27001 certification audit

You have set up an ISMS to ISO 27001 and want to make your level visible through a certificate? We work with several certification bodies and carry out ISO 27001 audits professionally and with an appropriate audit scope – including recertifications.

Our auditors know not only the standards but also the technologies and processes needed to reach a meaningful assessment. The certification body decides on the certificate.

Our expertise

ISMS (information security management system) under ISO/IEC 27001 are at the core of our work; our own ISMS is certified to ISO/IEC 27001:2022. secuvera has offered IT security consulting since 1988, and has been a BSI-certified IT security service provider since December 2011.

In-house, consultants and auditors work side by side: ISO 27001 lead auditors and IS auditors (IS-Revisoren) who work with several certification bodies. This audit experience feeds into our consulting.

Because consulting, internal audits and penetration tests come from a single source, the organisational and technical evidence for your ISMS can be aligned.

PIAQ certificate according to ISO/IEC 27001 for information security

Our own ISMS is certified

We do more than advise on ISO/IEC 27001. Our own information security management system is also certified to ISO/IEC 27001:2022. It covers our testing and consulting services and the associated support processes.

Read the publication on our certified ISMS
BSI-certified IT security service provider

IS consulting and IS audit: independently verified

secuvera is certified by the BSI (Federal Office for Information Security) as an IT security service provider for IS consulting and IS audit (IS-Revision). This evidence covers our consulting and audit services; certification decisions are made by the responsible certification bodies.

View certification for IS consulting and IS audit

Projektron on the way to ISO/IEC 27001 certification

Projektron describes how secuvera contributed to the ISMS with training, concept development, gap analysis and internal audits. The software manufacturer also reports on the transition to ISO/IEC 27001:2022 and certification by TÜV.

Read project report

yourIT: audits based on ISO/IEC 27001

Our auditors reviewed the internal processes, the premises and connections to cooperation partners. Certification to ISO/IEC 27001 was carried out by PÜG.

Read project report

Getting started

Assess certification readiness, plan the implementation

One-day workshop to get started

You are about to decide on introducing an ISMS to ISO 27001 and would like an initial assessment? In a one-day workshop on site or by video conference, we explain the standard and possible approaches. After you have presented your company and your processes, we review selected, representative topics. At the end, you receive an initial indication of which of these topics you already handle well and which need improvement.

Fixed price and individual adjustments

The workshop is offered at a fixed price of EUR 1,500.00 net. We are happy to plan individual adjustments or alternative ways of starting a project with you.

Discuss the status of your ISMS
Dividers fixing a position on the world map
Where does your ISMS stand today? An honest position check comes first.

The agenda for your introductory workshop

An initial assessment based on selected topics.

  1. Overview

    Brief introduction to information security management to ISO 27001

  2. Your organisation

    Understanding the organisation's requirements and defining the scope

  3. Selected topics

    Comparison with the required information security policies

  4. Management processes

    Comparison with the required information security management processes

  5. Initial assessment

    Indication of implementation time, effort and costs.
The ISMS needs internal owners

The introductory workshop looks at selected topics; it does not replace a full gap analysis. For certification, the ISMS is audited separately. Your internal owners must be able to continue the processes after the project.

Your questions about ISO 27001: implementation, audit and certification

How far are we from being ready for ISO 27001 certification?

This can only be assessed after reviewing scope, processes and evidence. In the one-day introductory workshop, we look at representative topics and give an initial assessment. A comprehensive assessment of the gaps requires a gap analysis designed for that purpose.

Do we need a gap analysis before ISO 27001 consulting?

If you need reliable knowledge of which requirements of the standard are already implemented, a gap analysis is a sensible starting point. For the basic decision on introducing an ISMS, the workshop may be enough at first. It examines selected topics and does not replace the full analysis.

How much do we need to contribute ourselves when building the ISMS?

Your responsible staff contribute their process knowledge, agree policies and run the processes that have been introduced. Management takes decisions on risks and resources. secuvera supports drafting and implementation; how much work can be done internally is reflected in the project plan.

How long does it take to introduce an ISMS to ISO 27001?

The scope, existing processes and the available involvement of your team determine the time required. An existing management system can provide a basis. After the initial assessment, we name the work still required and plan its sequence. A general certification deadline would not be reliable without this information.

Does secuvera support audit preparation?

Yes. Our services include internal audits, work on individual specialist topics and support during external audits. We look at whether policies, processes as actually practised and evidence fit together. The responsible certification body decides on certification.

Do you carry out certification audits to ISO 27001?

Yes, initial and recertification audits. Our team includes ISO 27001 lead auditors, and we work with several certification bodies. For planning, the existing certificate, the scope, previous findings and the intended date are important.

Who issues the ISO 27001 certificate?

The responsible certification body decides on certification and issues the certificate. secuvera provides the agreed audit services.

Articles on this topic (in German)

All 22 articles on the topic (in German)

How can we support you with ISO 27001?

A customer requires a certificate, an audit is coming up or risk management is still open? Tell us the reason and where you stand with your ISO 27001 implementation. For a certification audit, the scope, existing certificates and your target date also help us.

Discuss your ISMS project